Securinets Tekup mini-CTF:PCAP Master Revenge
TASK
Netcat Questions
Q1: Did you find credentials? What’s the user
Q2: Now give me his password
Q3: What was the first command he ran
Q4: What’s the malicious threat category
Solve
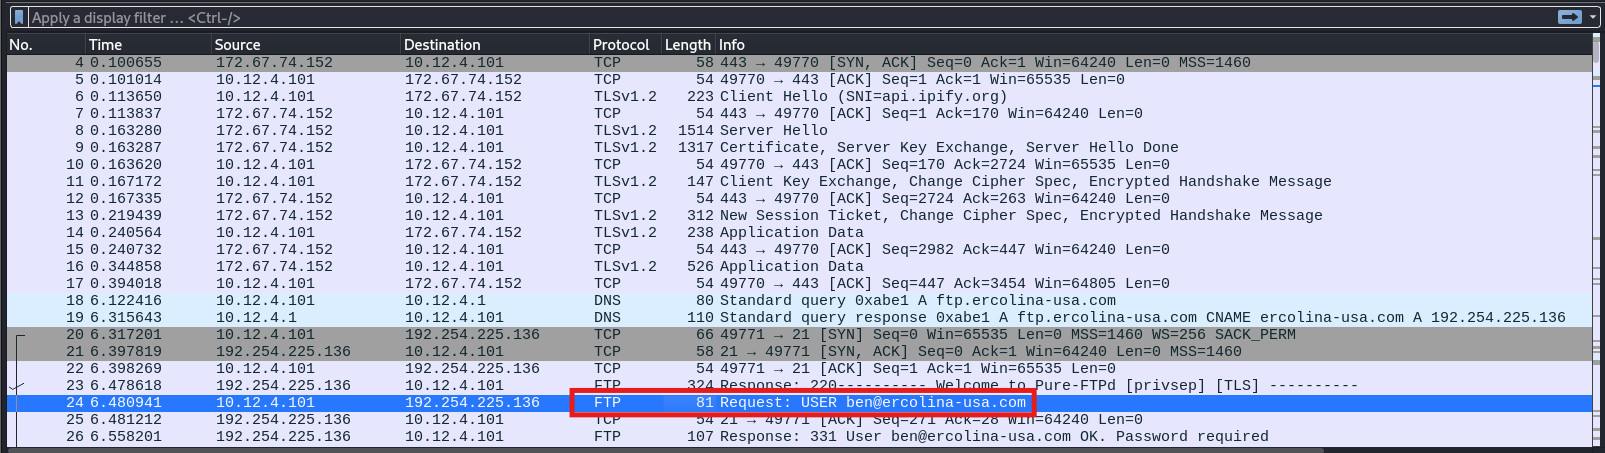
let’s open the file on Wireshark and start looking for teh answers Looking into the traffic we can see in line 24 an FTP request with a USER
Right click > Folllow > TCP Stream
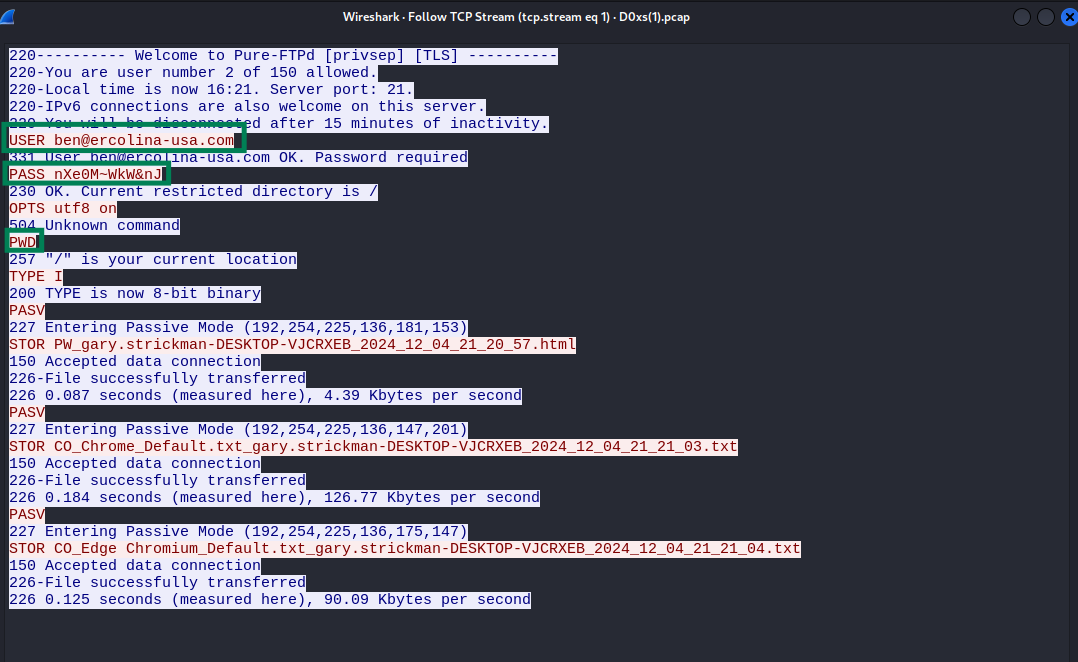
Now we can answer the three first questions, For the last question “What’s the malicious threat category” we need to understand what happend after this connection
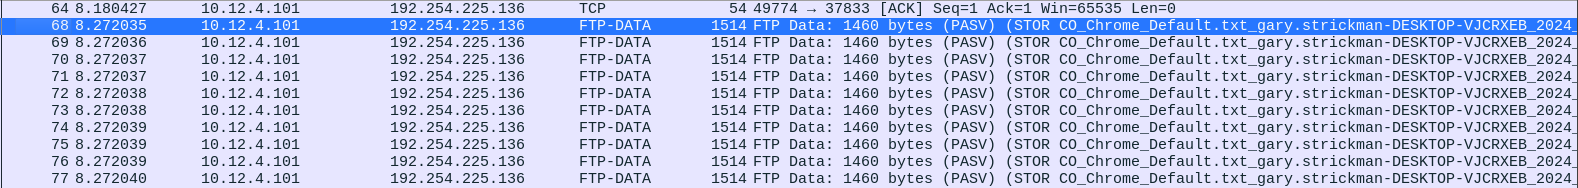
we can see too many FTP Data packets, we need to Follow TCP Stream to understand more
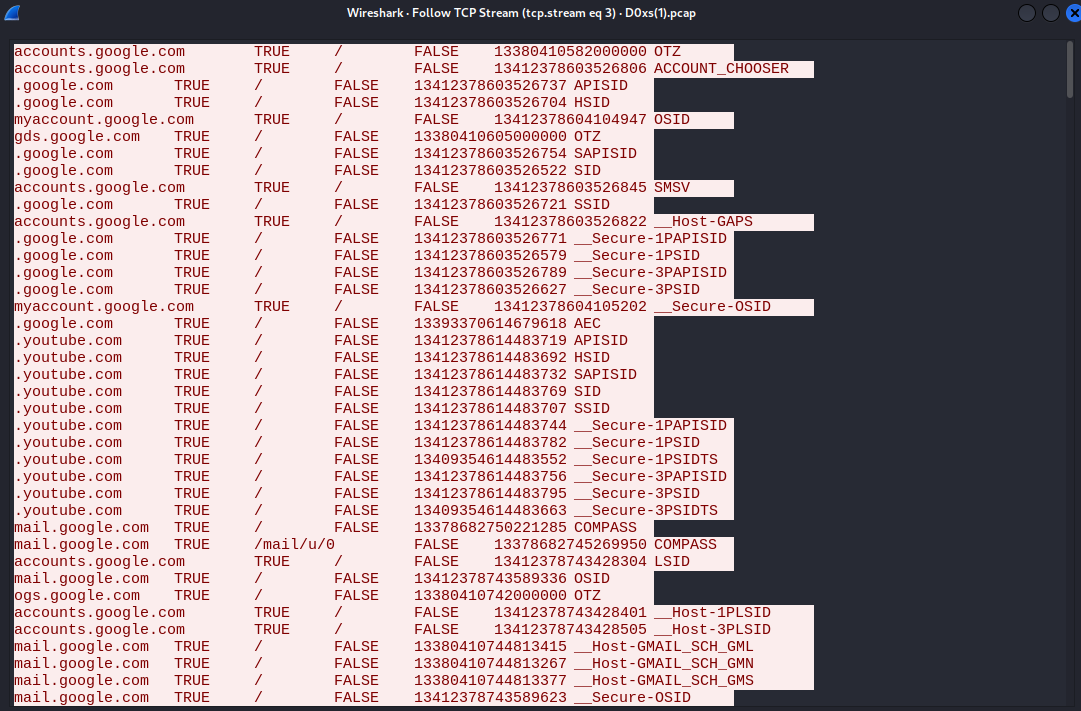
This type of data is a bit familiar its browser coockies, now we can connect dots, this is a browser coockies stealer who send them via FTP
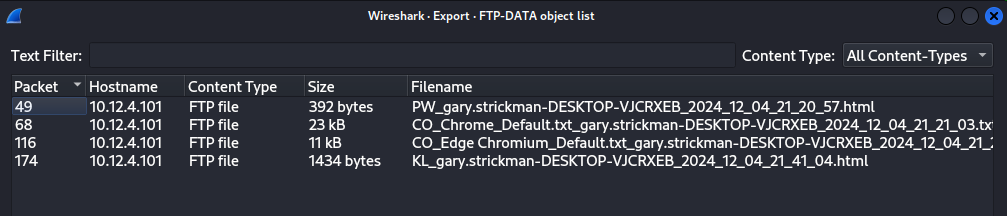
These type of keyloggers and stealers are categorized as “Trojans” Now we can answer all the netcat questions
Flag
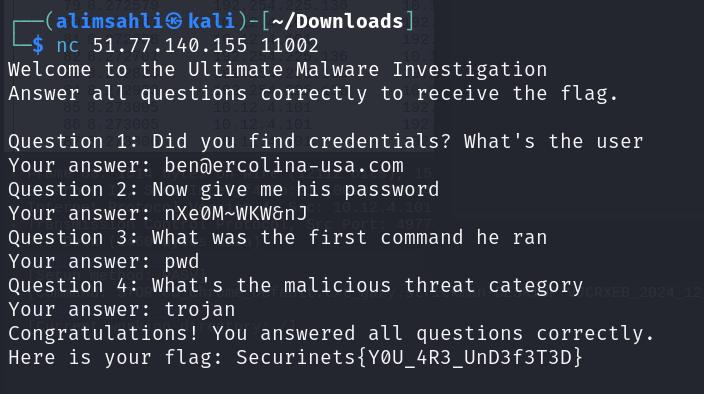
1
Securinets{Y0U_4R3_UnD3f3T3D}