Securinets Tekup CTF Kareem:Tajin b sebnekh
TASK
Solve
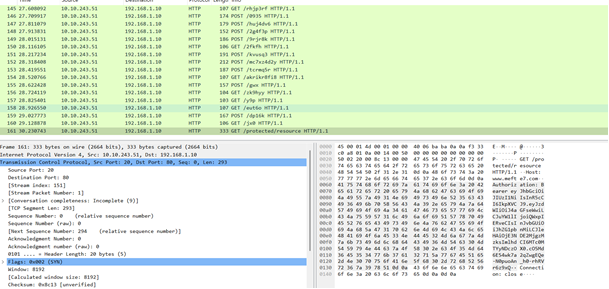
we have a random packets, lets start analysing them, we can a familier type of data in a packet its JWT token.
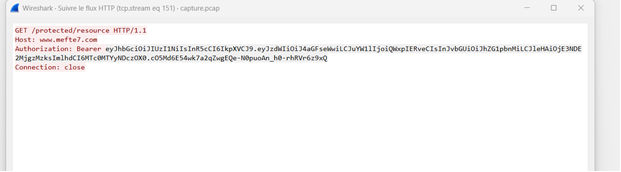
Maybe we need to crack it and get the secret, It may come handy later.
we can use this website to crack it website
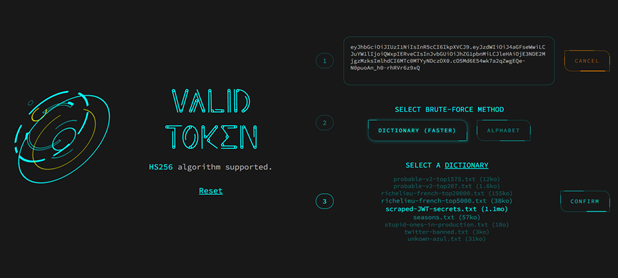
After craccking the secret is “babygirl” maybe we need this , we keep analysing the pcap. Filtring by the largest packets we can find a TCP that contain large data.
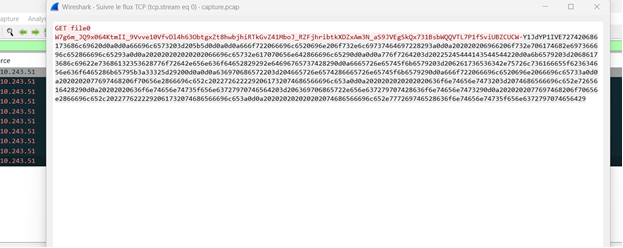
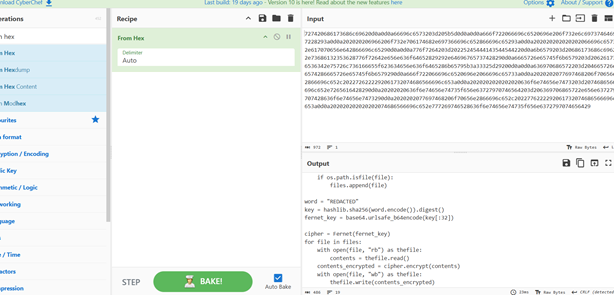
Decrypting it we can see the content of this file
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19

files = []

for file in os.listdir():
    if os.path.isfile(file):
        files.append(file)

word = "REDACTED"
key = hashlib.sha256(word.encode()).digest()
fernet_key = base64.urlsafe_b64encode(key[:32])

cipher = Fernet(fernet_key)
for file in files:
    with open(file, "rb") as thefile:
        contents = thefile.read()
    contents_encrypted = cipher.encrypt(contents)
    with open(file, "wb") as thefile:
        thefile.write(contents_encrypted)
Analysing this python script we can see that this script is using fernet to encrypt some files using a word to create a key, this word is the secret we found earlier in the jwt.
Now we need to find the files or their encrypted content so we can reverse it and get the flag. Here we have all tcp packets in the pcap file.
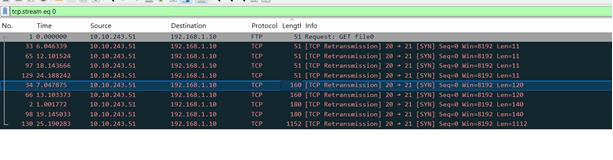
we need to create a script using scapy to extract the data from these packets
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
from scapy.all import rdpcap, TCP, Raw

def extract_tcp_data_to_txt(pcap_file, output_txt="extracted_tcp_stream_0.txt"):
    packets = rdpcap(pcap_file)
    extracted_text = ""

    for pkt in packets:
        if pkt.haslayer(TCP) and pkt.haslayer(Raw):
            extracted_text += pkt[Raw].load.decode(errors="ignore")
    with open(output_txt, "w", encoding="utf-8") as output_file:
        output_file.write(extracted_text)

    print(f"{output_txt}")

extract_tcp_data_to_txt("capture.pcap")
we will get the ecrypted files content with other missleading strings
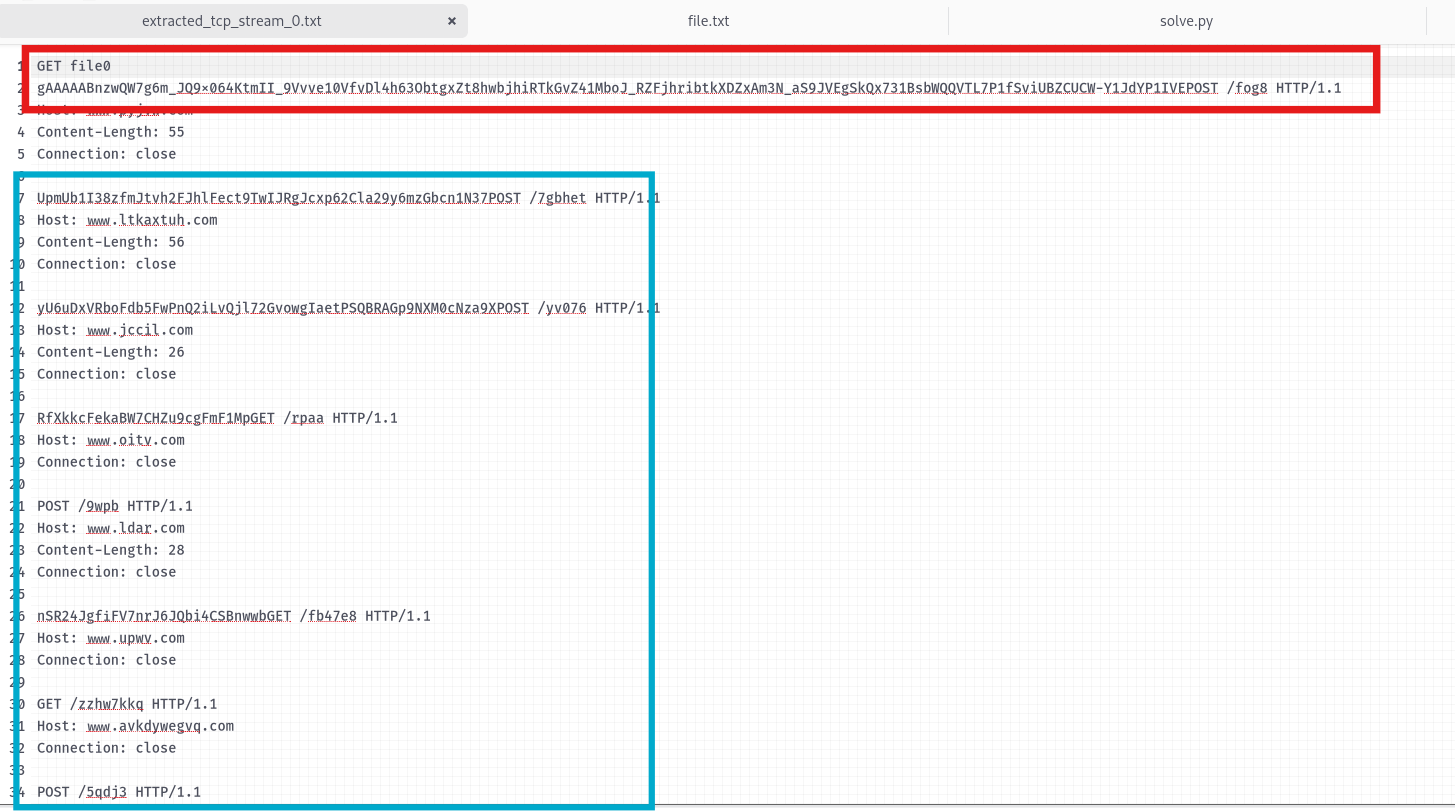
we need to extarct these strings to decrypt them with the revesed program we will create.
1
2
3
4
gAAAAABnzwQW7g6m_JQ9x064KtmII_9Vvve10VfvDl4h63ObtgxZt8hwbjhiRTkGvZ41MboJ_RZFjhribtkXDZxAm3N_aS9JVEgSkQx731BsbWQQVTL7P1fSviUBZCUCW-Y1JdYP1IVE
gAAAAABnzwQWp09ajpEFQ9Ad-7aiCE4H8B2igOihBN5hxSY4B06KdQ6cDEUSwMlzWwAwgLnE0g-NnpRwDR9bErLAS3nmVzGq68lBOYFT-9ayXSmoSWn_Mtc=
gAAAAABnzwQW4vWWuVowVljCnQaJI0uPLj3uZswx5QQRB2PMXK9JrggOzAMERaYKu0YAXaQthjEtVxRYziazsVwSpInRY8o7ezRW3lS6J58kHFoJEpgShQ4=
gAAAAABnzwQWxZ-oI4GMoK-QvIelxxIpS6lzj5yKkcVXGOqD8PBr1v4cXBjqrxHfwgcmn4euxTWAfBDxhvnhlM5GWDJ5Zv0Le7OUsrsHlYDkOgfJPC__HyenRDPGAO1Om0MKi-sykdWB
here is the decyption script
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
import hashlib
import base64
from cryptography.fernet import Fernet, InvalidToken


word = "babygirl"
key = hashlib.sha256(word.encode()).digest()
fernet_key = base64.urlsafe_b64encode(key[:32])
cipher = Fernet(fernet_key)


encrypted_strings = [
    "gAAAAABnzwQW7g6m_JQ9x064KtmII_9Vvve10VfvDl4h63ObtgxZt8hwbjhiRTkGvZ41MboJ_RZFjhribtkXDZxAm3N_aS9JVEgSkQx731BsbWQQVTL7P1fSviUBZCUCW-Y1JdYP1IVE",
    "gAAAAABnzwQWp09ajpEFQ9Ad-7aiCE4H8B2igOihBN5hxSY4B06KdQ6cDEUSwMlzWwAwgLnE0g-NnpRwDR9bErLAS3nmVzGq68lBOYFT-9ayXSmoSWn_Mtc=",
    "gAAAAABnzwQW4vWWuVowVljCnQaJI0uPLj3uZswx5QQRB2PMXK9JrggOzAMERaYKu0YAXaQthjEtVxRYziazsVwSpInRY8o7ezRW3lS6J58kHFoJEpgShQ4=",
    "gAAAAABnzwQWxZ-oI4GMoK-QvIelxxIpS6lzj5yKkcVXGOqD8PBr1v4cXBjqrxHfwgcmn4euxTWAfBDxhvnhlM5GWDJ5Zv0Le7OUsrsHlYDkOgfJPC__HyenRDPGAO1Om0MKi-sykdWB"
]


for encrypted_string in encrypted_strings:
    try:
        decrypted_contents = cipher.decrypt(encrypted_string.encode())
        print(decrypted_contents.decode())
    except InvalidToken:
        print("Decryption failed: Invalid key or corrupted data.")
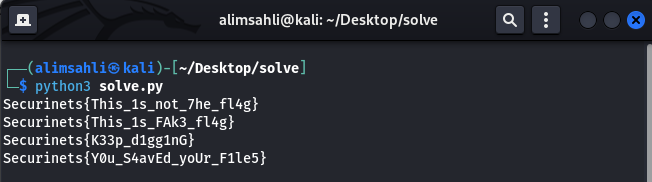
Flag
1
Securinets{Y0u_S4avEd_yoUr_F1le5}